Yes, a burner email can be traced, but rarely through the burner itself. In the court records we read, the persona addresses were not what identified their owners. What did was everything those addresses touched: a registrar login from a home connection, one VPN address used for a personal Google account and a persona account on consecutive days, a domain registration, a forum database that later leaked, and an everyday mailbox that was still in use.
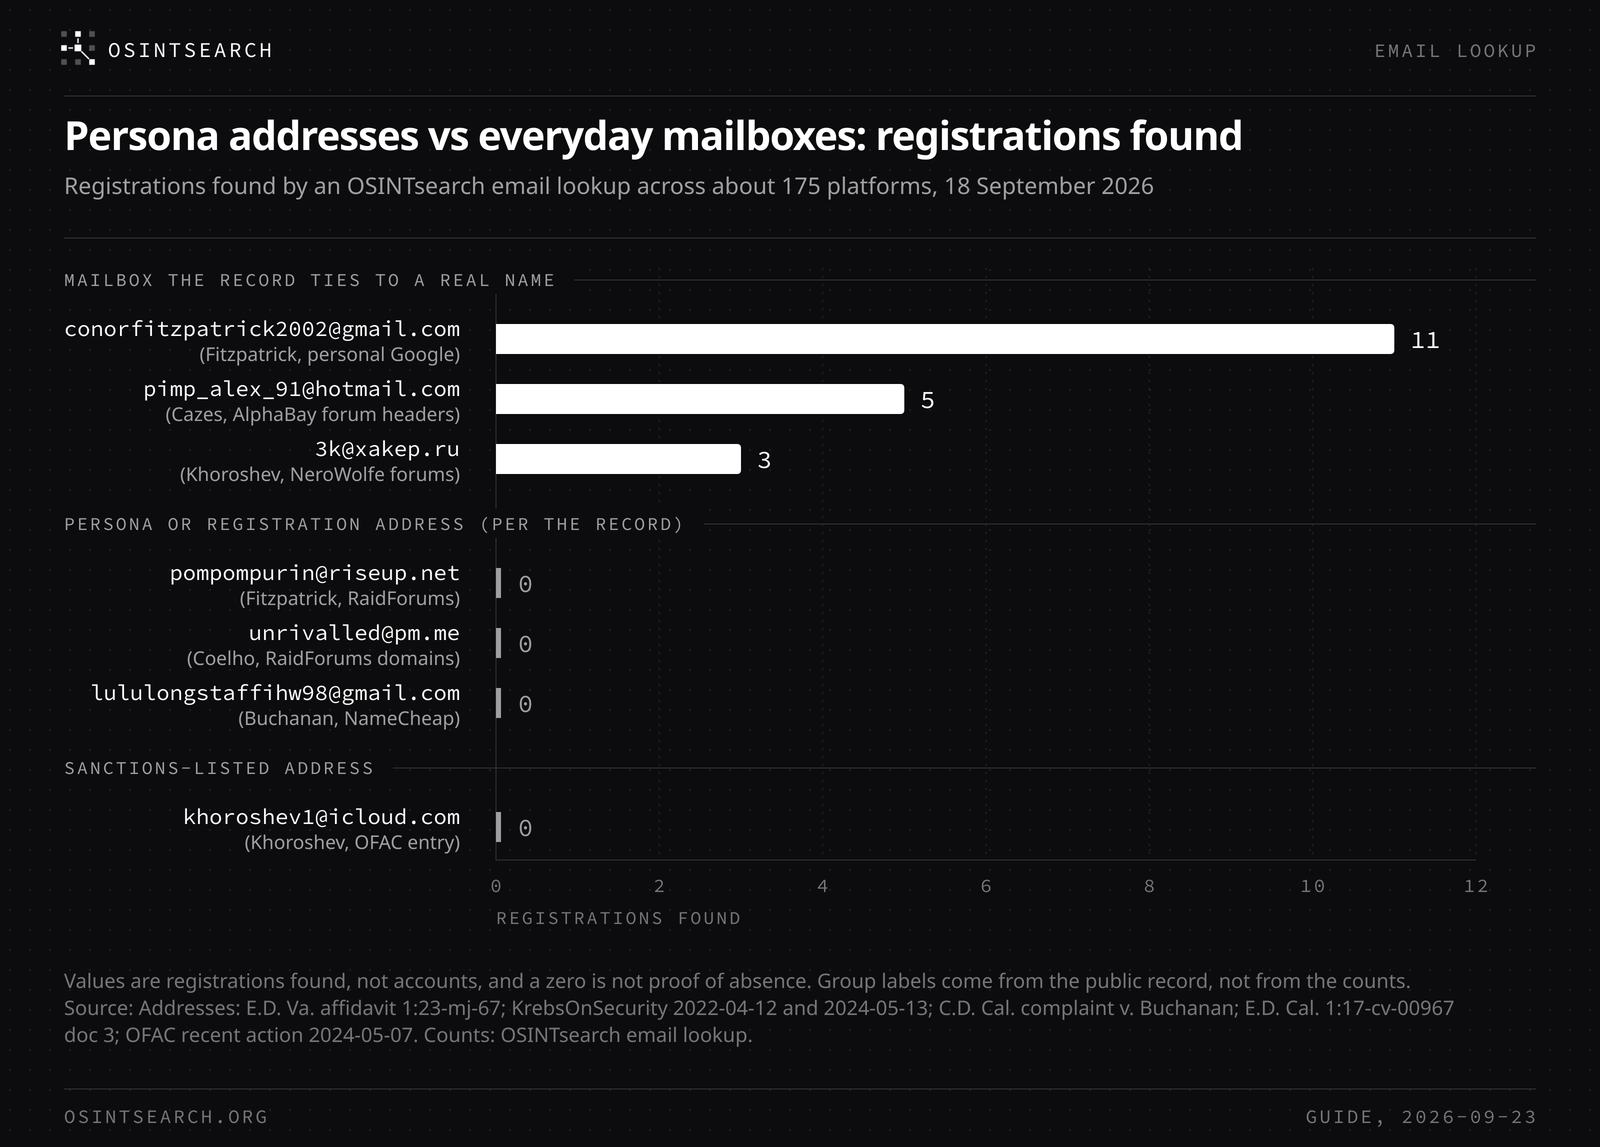
We took the addresses printed in those records and ran each one through an OSINTsearch email lookup across about 175 platforms on 18 September 2026. The lookup found no registrations for the persona and registration addresses, which is consistent with how the records describe them. The same people's everyday mailboxes told a different story.
What counts as a burner email
A burner is an address created for a narrow purpose and kept away from the owner's real life: no name in it, no reuse, no link to a phone or to other personal accounts. People usually pick a privacy-focused provider such as Proton or Riseup, or a free Gmail with a random-looking local part. A disposable inbox from a temporary-mail site is a weaker cousin: it lives for minutes, and on public-inbox services such as Mailinator anyone who types the address can read it.
Every subject below was publicly charged, convicted or sanctioned, and every identifier comes from a court filing, a Treasury sanctions entry or named reporting. People who are charged but not convicted are presumed innocent.
Four burners from the public record, and how each was traced
Pompompurin: a Riseup address and a shared VPN address
The FBI affidavit against Conor Brian Fitzpatrick, the BreachForums founder known as "Pompompurin", says [email protected] was his RaidForums registration address. The affidavit lays out many links, and one of them came from timing: per paragraph 64 of the affidavit, a VPN address that accessed his personal Google account on 7 March 2022 was used the next day to log into a Zoom account named "pompompurin" registered to the Riseup address. In paragraph 70 the agent notes that VPN and Tor "are occasionally misconfigured and expose the user's true IP address," and that a home internet address once logged into the pompompurin account.
An email lookup found no registrations for the Riseup address, consistent with its use as a persona address. The personal Gmail that Google records tie to him, [email protected], returned 11 registrations. Fitzpatrick pleaded guilty and was resentenced to three years in prison in September 2025.
Omnipotent: a Proton address the affidavit says he emailed to the FBI
Diogo Santos Coelho, charged as the RaidForums administrator "Omnipotent", had his devices searched at Atlanta's airport in June 2018. According to the government affidavit quoted by KrebsOnSecurity, he then called the lead FBI case agent and "used the email address [email protected] to email the agent." Investigators found the same address had registered rf.ws and raid.lol, the backup domains Omnipotent announced for the forum. He was arrested in the UK in January 2022 at the request of the United States. His extradition remains unresolved, and he is presumed innocent. An email lookup found no registrations for the Proton address. Per the affidavit, it was reached through a message to the investigator and a domain record.
TylerB: a random Gmail and a registrar login
The complaint against Tyler Robert Buchanan says the phishing domains in the case sat under one NameCheap account whose email was [email protected] (paragraph 35). On 4 May 2022 that account was logged into from an IP address that Virgin Media records showed was leased to Buchanan from January to November 2022 (paragraphs 37 and 38). An email lookup found no registrations for the Gmail across about 175 platforms, consistent with the complaint's description of it as a registration address, a point our Scattered Spider handle map also records. Buchanan pleaded guilty in April 2026.
Dendimirror: an address the complaint will not even print
The complaint against Maxim Rudometov, charged as a RedLine infostealer developer, withholds the address entirely and calls it "the Yandex Email Address." A US private security firm found it in a leaked database from a Russian-language hacker forum, where it had registered the "Dendimirror" moniker the complaint attributes to him. Investigators then linked it to other monikers and to "services used by RUDOMETOV in his personal capacity, such as Google and Apple." Rudometov is charged, has not been arrested, and is presumed innocent.
| Address | Role in the public record | Registrations found |
|---|---|---|
| [email protected] | RaidForums registration, reused for a Zoom account (affidavit para. 64) | 0 |
| [email protected] | Personal Google account tied to Fitzpatrick (para. 58 to 60) | 11 |
| [email protected] | Emailed the FBI agent; registered backup forum domains (Krebs) | 0 |
| [email protected] | NameCheap phishing-domain account (complaint para. 35) | 0 |
| [email protected] | Sender on AlphaBay forum welcome and reset emails (para. 21 and 22) | 5 |
| [email protected] | Listed in the OFAC sanctions entry for Dmitry Khoroshev | 0 |
| [email protected] | Registered more than a dozen NeroWolfe forum accounts (Krebs) | 3 |
The everyday mailbox is the one that talks
The mirror image of a persona address is a personal address pressed into criminal work. The AlphaBay forfeiture complaint says [email protected] was the sender on the AlphaBay forum's December 2014 welcome and password-reset emails, and that a 2008 tech-forum post by "Alpha02" was signed with the name Alexandre Cazes and that same address. Cazes died in Thai custody in July 2017, so the allegations were never tested at trial. The Hotmail address still returns 5 registrations today.
Treasury's sanctions entry for Dmitry Khoroshev, indicted as the alleged LockBit leader and presumed innocent, lists [email protected]; the lookup found no registrations for it. The address that did the identifying was older. Krebs reported that [email protected] was registered to more than a dozen NeroWolfe forum accounts and "was used in 2011 to create an account for a Dmitry Yurevich Khoroshev" on VKontakte. An email lookup on it today returns 3 registrations, one of them a GitHub account under the name of the NeroWolfe persona Krebs tied to him. The LockBitSupp post has the full picture.
The split can sit inside a single record. The SDN entry for Behzad Mesri, charged in 2017 over the HBO intrusion and presumed innocent, lists seven Gmail addresses. The lookup found no registrations for the two leetspeak ones, [email protected] and [email protected]. The address built on the alias in his 2017 indictment, [email protected], returns 3. The entry does not say who uses each address, so we read that only as a pattern.
Can a burner email be traced? Five ways it happens
- Provider and registrar records, under legal process. Proton, which built its service around privacy, is candid about this: "if you are breaking Swiss law, a law-abiding company such as Proton Mail can be legally compelled to log your IP address," it wrote in 2021. The Buchanan trace ran through a registrar's login log.
- Shared connections. One VPN address used for a personal account and a persona account joins them, as in the Fitzpatrick affidavit.
- What the burner registered. Domains, forum accounts and meeting accounts keep the address on file long after the owner forgets it.
- Leaked databases. Forum and game databases leak. Krebs traced the "HDGZero" persona through a leaked gaming-site user table; the man later convicted was sentenced to nearly eight years.
- Contact with the everyday. A recovery address, a message sent to a real person, a header on outgoing mail. Coelho's email to the agent, as the affidavit describes it, and the AlphaBay mail headers are both this kind of crossing.
The pillar post on how hackers get caught covers these failures across more cases.
If a burner email is harassing you
Keep the full message, including headers, and do not reply. Mail sent through the web version of Gmail, Outlook or Proton usually shows only the provider's servers in its headers, not the sender's own IP address, which is why headers mostly help the provider and the police rather than you. Run the address through an email lookup: a list of registrations suggests an everyday mailbox with a history, while few or no registrations fits an address made for this purpose, which means the useful evidence is more likely to be in the messages themselves. Try the local part as a username and check breach records, both covered in how to see behind an email and our breach check guide. Then report it to the mail provider and to the police. Providers answer legal process, which is how every trace in this post was made.
If you use a burner for privacy
Burners are a sensible habit for sign-ups, marketplaces and newsletters. The lesson from these records is to keep them separate: no personal recovery address, no login from the same connection as your main accounts, no reuse of the local part as a username. A free footprint audit of your main address shows what is already linked to you.
FAQ
Can police trace a ProtonMail account?
They can obtain what Proton is legally ordered to log, such as an IP address, though not encrypted message content. In the Coelho case, the affidavit ties the Proton address to him through what it was used for: an email to the FBI agent and the registration of forum domains.
Can a temp mail or disposable email be traced?
The service still sees the connection that opened the inbox and may keep logs, and on public-inbox sites anyone who knows the address can read the mail. What the address was used to sign up for stays on file with those services.
Can a Gmail made with a fake name be traced?
Often, yes. Google holds sign-up and login records and recovery details, and paragraph 60 of the Fitzpatrick affidavit shows Google records tying an account to a person. Buchanan's random Gmail was reached through NameCheap and Virgin Media records instead.
Can I find out who owns a burner email myself?
Rarely by name. You can learn what the address is registered to, whether it appears in breach data and whether its local part is reused as a username. Tying it to a person usually takes provider records.
Want to see what an address is connected to? Run a free email search on OSINTsearch: about 175 platforms in one sweep, with CSV, JSON or PDF export on paid plans.