LockBitSupp is the online persona that the United States, the United Kingdom and Australia say belongs to Dmitry Yuryevich Khoroshev, a Russian national charged in New Jersey as the developer and administrator of the LockBit ransomware operation. The public record prints eight email addresses tied to him. We ran all eight through an email lookup and ran the alias itself through a username search in September 2026. One mailbox still points to a GitHub account named after the forum persona Krebs tied to him, opened in 2011. A username search on the alias returns 22 exact-handle results, and the most eye-catching of them, a YouTube channel showing his name, is very probably not his.
Khoroshev is charged, not convicted, and he is presumed innocent. LockBitSupp has publicly denied being him, as KrebsOnSecurity reported. Nothing below identifies anyone new. Every identifier we searched was already published by a government agency or a named journalist.
Who is LockBitSupp, according to the public record
On 7 May 2024 the Justice Department unsealed a 26-count indictment in the District of New Jersey against "Dimitry Yuryevich Khoroshev," described as "also known as LockBitSupp, LockBit, and putinkrab, 31, of Voronezh, Russia." It alleges he ran LockBit from around September 2019 through May 2024, that the group attacked more than 2,500 victims in at least 120 countries, and that he personally received at least $100 million in developer shares. The counts carry a combined maximum of 185 years.
The same day, the Treasury's Office of Foreign Assets Control added him to the SDN list with the alias "LOCKBITSUPP" and two email addresses: [email protected] and [email protected]. The entry also prints a bitcoin address, two passport numbers and a tax ID, which we do not reproduce. The UK's National Crime Agency announced the joint sanctions with the US and Australia, and the State Department offered up to $10 million for information leading to his arrest or conviction, as the Justice Department release and the State Department announcement note.
The unmasking followed the February 2024 disruption of LockBit infrastructure led by the NCA. Since then the case has kept moving around him. Israel extradited alleged LockBit developer Rostislav Panev to New Jersey in March 2025, where he was detained pending trial. On 7 May 2025, a year to the day after the naming, LockBit's dark web affiliate panels were defaced with the message "Don't do crime CRIME IS BAD xoxo from Prague" and a panel database dumped, as BleepingComputer reported. In September 2025 the group announced LockBit 5.0, and Check Point Research counted a dozen organizations hit by the revived operation that month. We found no public report of Khoroshev's arrest as of September 2026.
How the persona was tied to a name
The indictment explains the charges, not the attribution. The clearest public reconstruction is Brian Krebs's May 2024 investigation, which starts from the two OFAC addresses and works backward with registration and breach data from DomainTools, Constella Intelligence and Intel 471. It is a model of patient, sourced work. In short:
- [email protected] registered at least six domains, including a business in Khoroshev's name. A phone number in those records matched Russian government documents naming him.
- A staircase-sales domain registered to that phone used [email protected] and [email protected], which shared one password in breach data. The domain's registrant was "Dmitrij Ju Horoshev" with [email protected], an address used in 2010 to open a hosting account for a Dmitry Yurievich Khoroshev from Voronezh.
- [email protected] belonged to a forum member called "Pin", who gave out an ICQ number on a second forum. That number led to "NeroWolfe" joining the Zloy forum in April 2011 with [email protected], from a Voronezh IP address.
- [email protected] used the same password as the stairwell mailbox, was registered to more than a dozen NeroWolfe forum accounts between 2011 and 2015, and in 2011 created a VKontakte account for "Dmitry Yurevich Khoroshev."
Krebs is careful about what this proves. "Does the above timeline prove that NeroWolfe/Khoroshev is LockBitSupp? No," he writes. The link from the forum trail to the LockBit persona rests on the government's evidence.
What the eight published addresses return today
An email lookup checks whether an address is registered on about 175 services and, where a service exposes it, returns the public handle attached. Here is what the eight addresses returned in September 2026.
| Address | Published by | Registrations found | What stands out |
|---|---|---|---|
| [email protected] | Krebs | 3 (GitHub, Dropbox, Eventbrite) | GitHub account on the handle "nerowolfe", created November 2011 |
| [email protected] | Krebs | 3 (X, Dropbox, Microsoft) | X reports the address is in use |
| [email protected] | OFAC | 2 (Yandex, WordPress) | The domain-registration mailbox is still live |
| [email protected] | OFAC | 0 | No registrations found |
| [email protected] | Krebs | 0 | The 2011 Zloy address |
| [email protected] | Krebs | 0 | |
| [email protected] | Krebs | 0 | |
| [email protected] | Krebs | 0 |
The strongest result is the first row. The address Krebs ties to a dozen NeroWolfe forum accounts and a 2011 VK profile is also attached to a GitHub account whose handle is "nerowolfe." That reproduces the reporting from a different platform. The account was opened on 5 November 2011, the same year Krebs places NeroWolfe on Zloy and Verified, and nearly eight years before LockBit existed, which rules out a squatter reacting to the 2024 news. It still does not prove who controls the account today; GitHub does not verify names. It does show the mailbox was used to register a developer account under the same persona, which fits the C and C++ coder Krebs describes.
The second finding is that [email protected], a mailbox from a 2010 hosting signup, is still bound to an X account and to Dropbox and Microsoft accounts.
The address Treasury printed first, [email protected], had no registrations found. In this case, as in others we cover in how hackers get caught, the useful trail ran through other working mailboxes such as [email protected] and [email protected].
The LockBitSupp username: 22 results in three eras
A username search on "lockbitsupp" across about 760 platforms returned 22 exact-handle results. Dates matter more than display names here, because the alias was famous long before Khoroshev's name was. The persona has used that name since LockBit's affiliate program launched around January 2020, and it drew worldwide coverage when LockBit's sites were seized in February 2024.
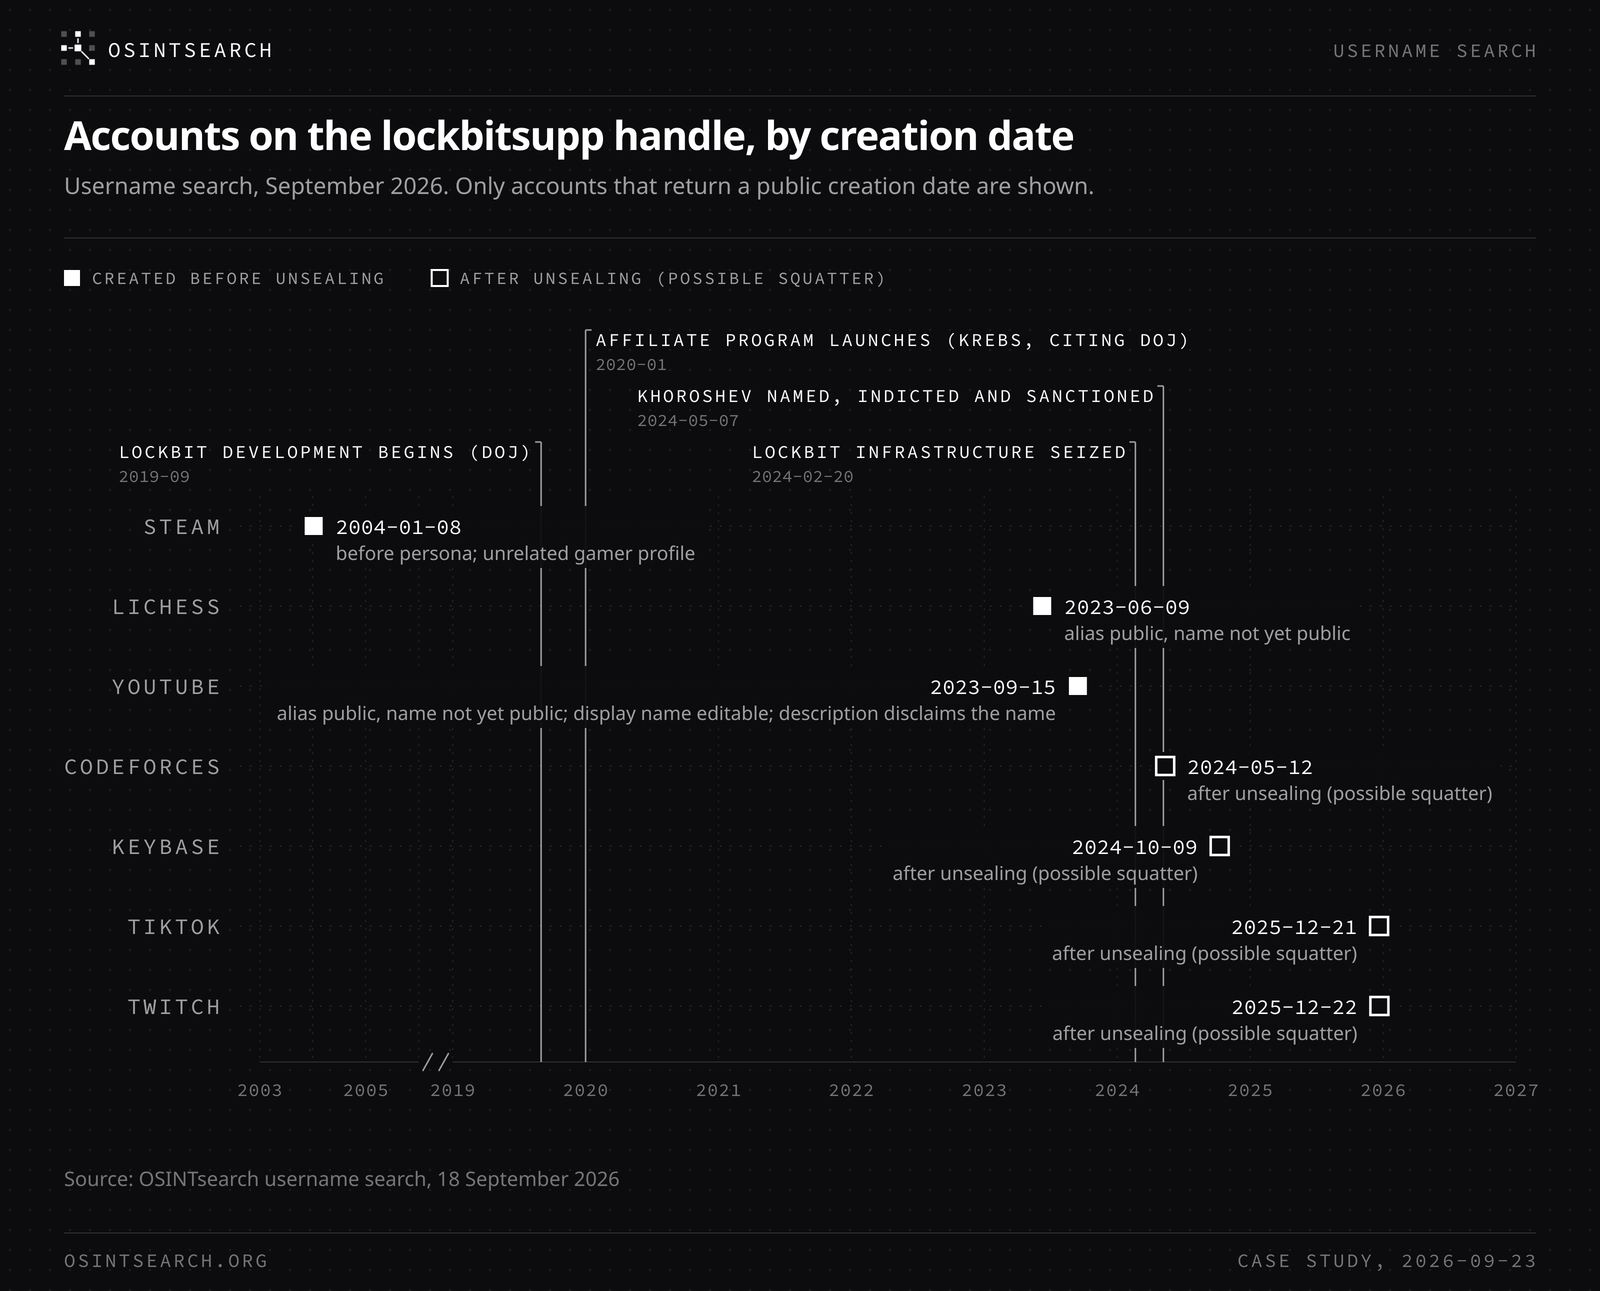
Before the persona existed. A Steam account on the handle was created on 8 January 2004 and displays an unrelated gamer's name and links to streaming profiles, with nothing that touches LockBit. Steam custom profile URLs can be changed at any time, so the handle may have been set long after 2004.
After the alias was famous but before the unsealing. A Lichess account dates from 9 June 2023. A YouTube channel dates from 15 September 2023, and its display name currently renders Khoroshev's full name in Japanese katakana next to "LockBitSupp Ch". That looks striking, but it is not evidence. Channel names can be edited at any time, so the date tells you when the channel was opened, not when the name was typed. The channel's own description undercuts the link further: it presents the channel as a gaming and online-drama channel whose owner says the nickname is not their real name. The likeliest reading is a fan or joke channel, with the name probably added after it became public in May 2024.
After the unsealing. A Codeforces account was created on 12 May 2024, five days after the indictment was unsealed. A Keybase account followed on 9 October 2024. A TikTok account with a display name using Khoroshev's first name was created on 21 December 2025 and a Twitch account the next day, 22 December 2025. A StreamElements profile shares the Twitch avatar, so those two belong to one holder. Every account created after 7 May 2024 on a globally reported criminal alias should be treated as a possible squatter or impersonator.
The remaining results are undated presence on gaming, coding and chat services: GitHub, Telegram, Threads, Snapchat, Xbox, Minecraft, a LeetCode profile that links to the GitHub account, and a handful of others. One more result is a handle-derived mailbox check, not an account. None links verifiably to the record.
Why "nerowolfe" is a noisy search on its own
Nero Wolfe is Rex Stout's fictional detective, so the handle has been claimed by readers for decades. The username search returned 113 exact matches, with display names belonging to many unrelated people and locations on several continents. Only one of them, the GitHub account reached through [email protected], is anchored to the public record. That is the general lesson in threat actor attribution: an email anchor beats a handle match every time. The Scattered Spider handle map shows the same effect across a whole group, and our Galochkin post shows the opposite case, a rare handle where the username search carried the name.
FAQ
Who is LockBitSupp?
LockBitSupp is the persona of LockBit's administrator. US, UK and Australian authorities named Dmitry Yuryevich Khoroshev of Voronezh as the person behind it on 7 May 2024. He is indicted, sanctioned and presumed innocent, and LockBitSupp has denied the identification.
Has Khoroshev been arrested?
Not as of September 2026, as far as any public report we found shows. The State Department's reward of up to $10 million remains the standing offer, and LockBit has kept operating, including a 5.0 release in September 2025.
Is the LockBitSupp YouTube channel his?
There is no evidence it is. It was created in September 2023, but display names can be changed later, and the channel's own description presents it as a gaming and drama channel run by someone who disclaims the name.
What was NeroWolfe?
A forum persona active from 2011 to around 2016 that Krebs tied to Khoroshev through shared email addresses, an ICQ number and a reused password. An email lookup on the persona's address still reaches a GitHub account on that handle, created in November 2011.
Check the record yourself
Every identifier here came from OFAC, the Justice Department or KrebsOnSecurity, and every result can be reproduced. OSINTsearch returns the platform, handle, display name, creation date and linked accounts for each hit, and exports the whole sweep to CSV, JSON or PDF. The free plan runs a full sweep, so you can run an email or username search on OSINTsearch and read the dates for yourself.